
Wow! This feels like one of those debates that never quite goes away. I remember the first time I put BTC onto a tiny card-sized device; somethin’ about the weight of that decision stuck with me. The idea of cold storage sounds dry, but the reality is visceral — your private keys can be a single physical object you touch. My instinct said that was powerful, and then I started poking around the UX and threat models more carefully.
Here’s the thing. Mobile apps are convenient. They are also, in my experience, often the weakest link. Apps get permissions, push notifications, and sometimes sketchy clipboard behavior. On one hand a phone gives speeds and convenience; on the other hand, though actually, the attack surface grows fast. Initially I thought you could just rely on a secure enclave, but then I saw how social-engineering and malware still found ways in.
Really? The simplest stories are often the truest. A stolen phone with unlocked apps might not get your cold storage seed, but an app that syncs keys or a backup service will. So the question I kept circling was: can we have the convenience of a pocket device with the security of offline keys? That pushed me toward smart-card approaches — little immutable things that behave more like a credit card than a mini computer.
Whoa! Smart cards feel familiar. They’re tactile, durable, and they don’t run arbitrary third-party code. Medium-length explanation: they typically store keys in secure elements and only sign transactions when asked, preventing direct key extraction. Longer thought: when you pair a smart-card with a dedicated mobile app that only prepares unsigned transactions, then hands the payload off to the card for signing before broadcasting, you create a strong separation that reduces many common attack vectors.
Okay so check this out—there are tradeoffs. Some smart-card wallets are super minimalist and have no battery, which is great. They rely on NFC or contact to interact. Others add biometrics or screens but increase complexity. I’m biased toward simplicity; simpler attack surface usually means fewer surprises. (oh, and by the way… that simplicity is what keeps me coming back to cards.)
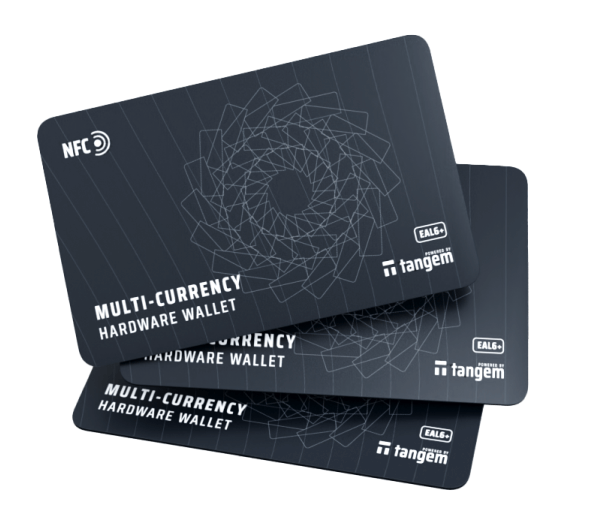
Why cold storage with a smart card often wins
Short bursts: Seriously? Yes, seriously. Medium description: cold storage keeps private keys offline, and smart cards make that offline state physical and persistent. Longer reflection: unlike paper wallets that degrade or seed phrases that can be copied incorrectly, a tamper-resistant card stores keys in hardware that resists probing and extraction, and that dramatically lowers risk for non-technical users.
On one hand, you get robustness — on the other hand, you must trust the manufacturing and secure element. My experience shows that open design and audited chips matter. Initially I thought closed-source was fine if the company had a good track record, but then a few supply-chain stories made me re-evaluate. Actually, wait—let me rephrase that: trust is layered, and audits plus transparency reduce the unknowns.
Check this: recovery methods matter more than you think. If a card is lost or damaged, having a clear, tested recovery workflow saves the day. Some folks store seeds in a steel plate, others split secrets with Shamir backup. It’s personal. I’m not 100% sure one method fits all, though in practice a simple seed backup that’s rehearsed is usually enough.
Here’s a concrete example from my own mistakes. I once set up a smart-card wallet and skipped testing the recovery phrase. Later, a card bent in my wallet and wouldn’t respond. Panic. I had to use the recovery to restore funds. That small oversight cost me a sleepless night. Lesson: test the whole process end-to-end, including the restore, before you trust a device with real funds.
The mobile app: not the enemy, but the partner
Hmm… mobile apps get a bad rap, but they are essential. A good app serves as a transaction composer and a UX bridge. It builds the unsigned transaction and hands it to the card for signing, then broadcasts. Short point: the app should never hold or export private keys.
Medium point: look for apps with clear permission boundaries and local-only storage. Super long thought: when an app uses only local, ephemeral transaction data, sends no sensitive info to remote servers, and presents a verifiable signing confirmation that matches the card’s display (if available), you get a user experience that feels modern and yet preserves the cold-storage model.
There are products that blur lines. Some advertise “cold” but sync backups to cloud. That part bugs me. Do your homework—watch for automatic backups, remote key access, or anything that creates a remote copy. I’m biased, but if the company suggests cloud sync for keys, step back and consider options.
One device type I’ve used and recommend investigating is a smart-card hardware wallet that pairs with mobile apps seamlessly. For example, the tangem wallet approach is elegantly simple: the card stores keys, and the app acts only as an interface for signing and broadcasting. It felt natural to me, and the onboarding was surprisingly fast.
Threat models and practical advice
Short: Threat modeling is essential. Medium: Define what you’re protecting against—physical theft, malware, state-level actors, or simple user error. Long: Different threat models justify different setups: a person protecting a small stash from thieves has a very different setup than someone protecting a multi-million-dollar treasury from targeted attacks.
On physical theft: a card in a hidden wallet, maybe split between locations, reduces single-point failure. For malware: using a dedicated offline device or verifying transaction details on a secondary screen helps. For nation-state level threats: hardware provenance and supply-chain scrutiny become critical — think audited chips, secure manufacturing, and independent reviews.
Another practical tip: practice your recovery plan annually. Sounds obvious, but people forget. Recover on a spare device, confirm balances, then wipe. Repeat. Also label things in a way that doesn’t attract attention — no “crypto backup” on the safety deposit box, please.
User experience and adoption
Long thought: the best security is the one people will actually use. If a system is clunky, people will bypass it. So designing for low friction — good mobile pairing, clear prompts, easy recovery — increases real-world safety. My gut says that products leaning into the credit-card form factor are closer to what mainstream users will accept.
Short aside: tangibility helps. A card you can pass to a trusted family member, or place in a safe, feels real. Medium: for many users, this physical reassurance beats abstract seed phrases or phrases stored in a password manager. And, yes, there are downsides — physical loss, manufacturing trust — but those are manageable if you plan.
FAQ: Quick answers to common questions
Is a smart-card wallet truly “cold”?
Mostly yes. The private key stays in secure hardware and is never exported. The mobile app only prepares transactions. However, be mindful of any backup or cloud features that might reintroduce online exposure.
What if my card gets damaged?
Recover using the seed or the recovery method provided by the wallet. Test the recovery beforehand and consider splitting backups (Shamir, multisig, or geographic separation) depending on how much you hold.
Which card should I buy?
Look for audited hardware, secure element usage, clear UX, and a trustworthy company. If you want a compact, tested option with simple mobile pairing, check the tangem wallet as a starting point for research.
